Mapping NIST Controls Across Cloud Providers
NIST frameworks define outcomes; AWS, Azure, and Google Cloud supply services and evidence that help implement them. Effective mapping connects each requirement to accountable owners, technical controls, inherited responsibilities, monitoring signals, and verifiable audit evidence.
How NIST Strengthens Cloud Security: Control Mappings, CSP Responsibilities, and Risk Management
Cloud adoption continues to accelerate across every industry, and with it comes an increasing need for standardized security expectations. While Cloud Service Providers (CSPs) such as AWS, Microsoft Azure, and Google Cloud Platform (GCP) offer powerful infrastructure and shared responsibility models, it is the National Institute of Standards and Technology (NIST) that provides the foundational security frameworks to help organizations evaluate risk, design secure architectures, and maintain compliance.
NIST’s frameworks, baselines, and control catalogs—including NIST SP 800-53, 800-171, CSF (Cybersecurity Framework), and 800-37 (RMF)—have become the de facto standards that both federal and private-sector organizations depend on to secure workloads in the cloud. CSPs directly reference these frameworks in their own security baselines and certification programs, creating a common language for cloud risk management.
This article explores how NIST and CSPs align, how controls map across cloud architectures, and how NIST frameworks help secure modern cloud environments.
1. The Role of NIST in Cloud Security
NIST does not enforce regulations; instead, it publishes authoritative, vendor-neutral guidance used across the U.S. government and an increasing portion of the private sector. Its primary focus areas include:
Security controls (NIST SP 800-53)
Risk management processes (NIST SP 800-37)
Protection of controlled unclassified information (CUI) (800-171)
Cybersecurity maturity and resilience frameworks (NIST CSF 2.0 (with CSF 1.1 retained only for historical mappings))
Cloud security standards and architectures (SP 800-144, SP 800-210, SP 500 series)
For cloud environments, NIST provides security and governance foundations that integrate naturally with CSP infrastructures.
2. CSPs and NIST: The Shared Responsibility Model
Every major CSP follows a shared responsibility model:
CSP is responsible for: Physical security, compute/network/storage infrastructure, hypervisor, some managed service security, logging pipelines, hardware hardening, global network security.
Customer is responsible for: Identity & access management, data protection, workload and application configuration, OS-level patching (unless managed), encryption use, network design, monitoring, and incident response.
NIST frameworks help organizations translate these responsibilities into concrete security controls.
For example:
NIST SP 800-53 control AC-2 (Account Management) maps to:
AWS IAM, Microsoft Entra ID, GCP IAM configuration
MFA enforcement
Role-based access control
Privileged access policies
NIST SC-13 (Cryptographic Protection) maps to:
AWS KMS, Azure Key Vault, GCP KMS
TLS enforcement
Encryption at rest with managed keys
NIST AU-6 (Audit Review, Analysis, and Reporting) maps to:
AWS CloudTrail
Azure Monitor / Sentinel
GCP Cloud Logging & Cloud Audit Logs
This alignment allows agencies and enterprises to confidently build secure cloud environments based on proven controls.
3. How CSPs Adopt and Map NIST Controls
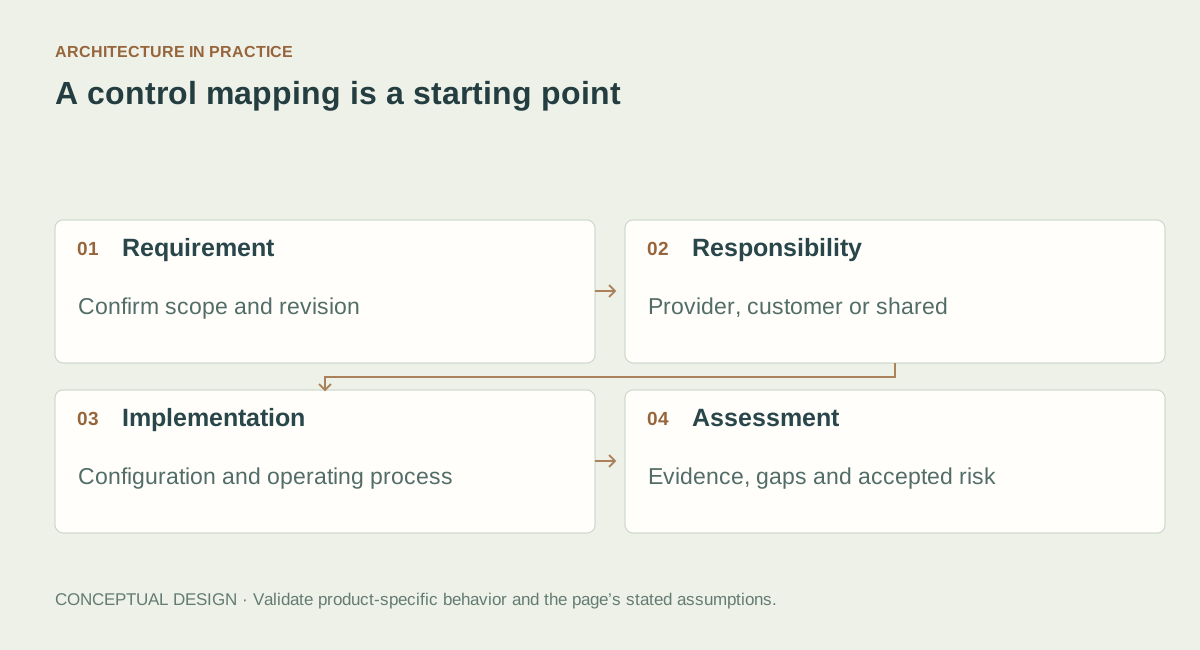
CSPs publish their own NIST control mappings, which help organizations understand exactly how cloud services satisfy NIST requirements. For example:
AWS
AWS NIST 800-53 Security Compliance Matrix
AWS Artifact provides FedRAMP/NIST audit packages
Managed services (e.g., S3, RDS, Lambda, EC2) include mappings to control families like AC, SC, SI, AU, CM, MP, and IR.
Azure
Microsoft cloud security benchmark maps directly to:
NIST 800-53
NIST CSF
CIS controls
Controls are built into Azure Policy, Defender for Cloud, and Azure Monitor.
GCP
GCP Compliance Resource Center includes:
NIST SP 800-53 Rev 5 mappings
FedRAMP High/Moderate authorizations
GCP services integrate with Google Security Operations/SCC for continuous control monitoring.
These mappings make it easier for organizations to document compliance, implement secure architectures, and integrate controls into continuous monitoring systems.
4. Key NIST Control Families That Secure Cloud Environments
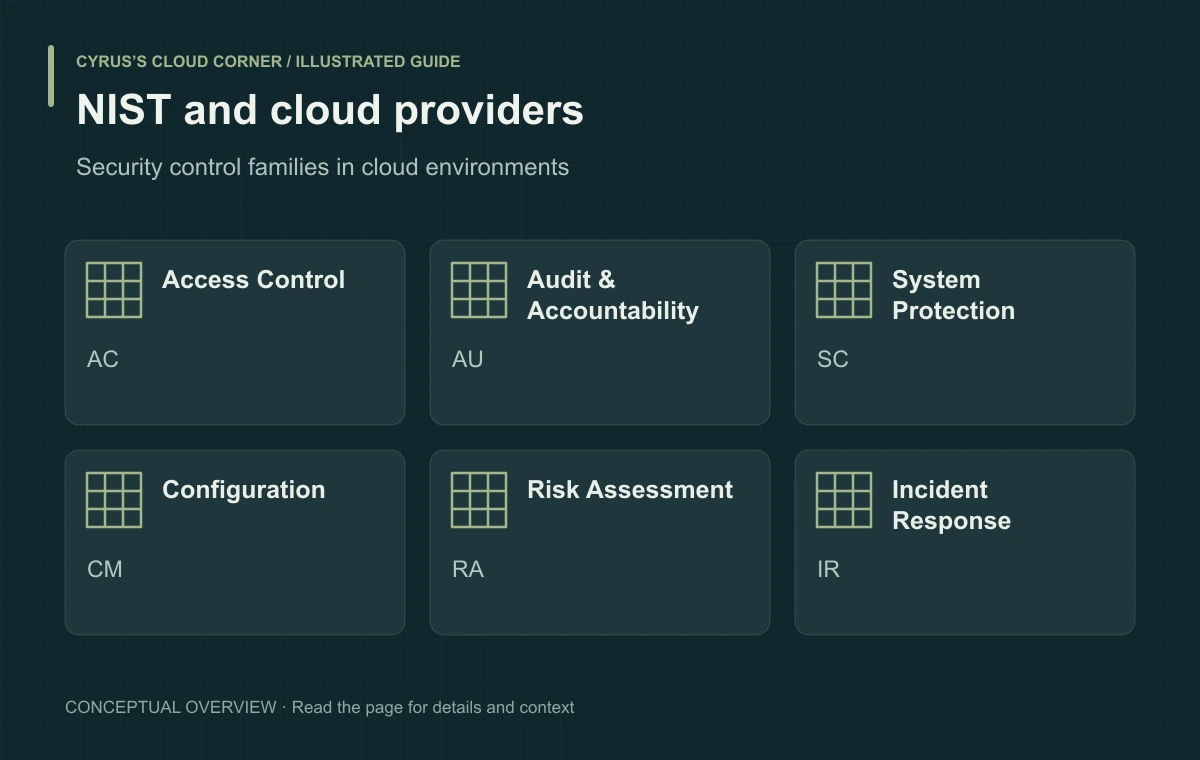
While NIST SP 800-53 includes 20 control families, several are especially critical for cloud security:
1. Access Control (AC)
IAM policies
MFA
Privileged access management
Conditional access
2. Audit & Accountability (AU)
Logging
Log retention
Log integrity
Security monitoring
3. System & Communications Protection (SC)
Encryption
Network segmentation
API security
Boundary protection
TLS enforcement
4. Configuration Management (CM)
Secure templates (CloudFormation, ARM, Terraform)
Baseline images (AMIs, VM images)
Version control
Drift detection
5. Risk Assessment (RA)
Vulnerability management
Threat modeling
Asset inventory
Continuous monitoring
6. Incident Response (IR)
Playbooks
SIEM/SOAR integration
Forensic readiness
Automated alerts
7. System Integrity (SI)
Malware defense
Patch management
File integrity monitoring
Runtime protection
Each of these NIST control families maps tightly to native CSP tools.
5. NIST Frameworks That Directly Strengthen Cloud Security
✔ NIST SP 800-53: Security and Privacy Controls
Defines the world’s most widely adopted control catalog.
✔ NIST Risk Management Framework (RMF) – SP 800-37
Provides a lifecycle for assessing, authorizing, and continuously monitoring systems in the cloud.
✔ NIST Cybersecurity Framework (CSF 2.0)
Used for enterprise risk posture; aligns with cloud practices such as:
Identify → Asset inventory, tagging, classification
Protect → IAM, encryption, boundary control
Detect → Monitoring, SIEM
Respond → IR workflows
Recover → Backups & resilience
✔ NIST SP 800-171
Used for protecting CUI in cloud systems (important for DFARS, DoD contractors).
✔ NIST Cloud Security Guidelines (SP 800-144, SP 800-210)
Provide cloud-specific threat models, architectural guidance, and security requirements.
6. How NIST Improves Cloud Security in Practice
NIST provides cloud security through:
1. Standardized Security Baselines
Organizations can adopt standardized configurations aligned to NIST, reducing risk from misconfiguration.
2. Improved Governance
NIST helps CISOs and security teams ensure cloud deployments meet compliance, audit, and reporting requirements.
3. Continuous Monitoring
NIST’s RMF and CSF integrate with CSP tools like:
AWS Security Hub
Azure Security Center / Defender for Cloud
GCP Security Command Center
4. Risk-Based Decision Making
NIST SP 800-30 and SP 800-37 guide how to assess cloud-specific threats such as:
IAM misconfiguration
Identity sprawl
Public S3 bucket exposure
Lateral movement risks
Overprivileged roles and service accounts
5. Protection of Sensitive Data
NIST’s cryptographic guidance aligns with cloud-native encryption, key management, and tokenization.
7. Conclusion: Why NIST is Essential in Securing the Cloud
As cloud environments grow more distributed, dynamic, and data-rich, the need for standardized security increases. NIST frameworks offer:
A common language for cloud security
Universal baseline controls
A defensible and audit-ready risk management process
Practical guidance that integrates with AWS, Azure, and GCP security services
Cloud providers deliver powerful tools—but NIST gives organizations the structure, rigor, and confidence needed to implement them securely.
Together, NIST and CSPs create a robust ecosystem that supports secure cloud adoption across government, enterprise, and critical infrastructure sectors.
Current guidance · October 25, 2026
CSF 2.0 has six functions: Govern, Identify, Protect, Detect, Respond, and Recover. SP 800-53 Rev. 5 is a control catalog; SP 800-171 Rev. 3 addresses CUI in nonfederal systems. The revision required by a particular contract or assessment must be checked separately. A cloud service mapping does not prove that a control is implemented.