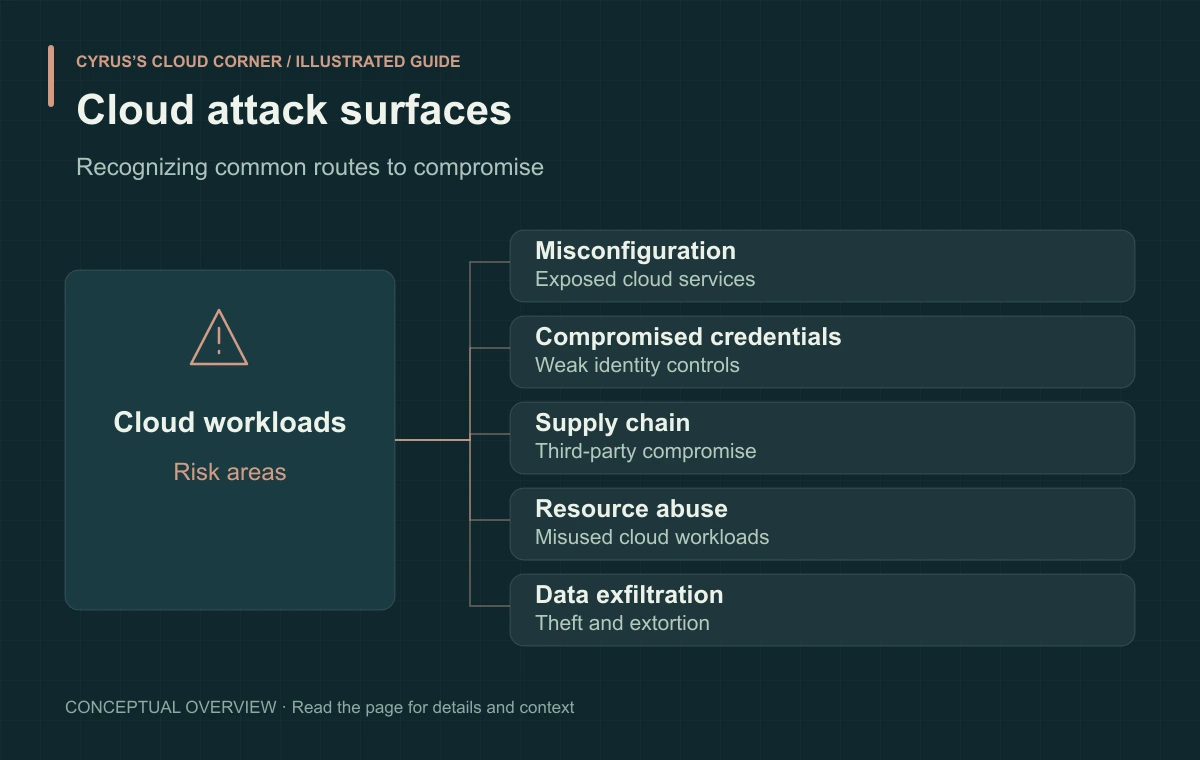
Historical incidents and research disclosures show different failure modes across customer applications, provider infrastructure, identity systems, and software supply chains. The defensive lessons below are editorial recommendations, not findings that every victim had the same weakness.
Content reviewed: October 25, 2026
Capital One · 2019
Capital One disclosed unauthorized access to customer and applicant information. The case illustrates why application exposure, workload identity permissions, and sensitive-data access must be assessed together. Avoid treating a storage provider’s controls as a substitute for the application’s authorization design.
SolarWinds / SUNBURST · 2020
Compromised Orion updates delivered a backdoor through a trusted software distribution channel. Review build provenance, privileged management connectivity, identity federation, and the ability to investigate activity after a supplier compromise.
Codecov · 2021
An attacker modified the Bash Uploader to expose information from customer CI environments. Treat pipeline secrets and downloaded build tools as production trust dependencies. Use controlled dependencies and short-lived credentials, and rotate affected secrets after exposure.
Kaseya VSA · 2021
The directly compromised VSA installations were the on-premises product; the incident should not be described as a compromise of the VSA SaaS platform. Ransomware spread through trusted remote-management relationships. Separate management privileges and rehearse coordinated recovery with service providers.
Exchange / HAFNIUM · 2021
Microsoft documented exploitation of vulnerabilities in on-premises Exchange Server. This is distinct from the 2023 Exchange Online intrusion. Maintain exposed-system inventories, patch critical vulnerabilities, and investigate persistence rather than assuming patch installation removes an existing compromise.
Cosmos DB / ChaosDB · 2021 research disclosure
Researchers disclosed a vulnerability affecting Cosmos DB key access. A demonstrated research exposure is not evidence that every potentially affected customer suffered malicious exploitation. Review provider notices, key rotation instructions, and the scope of the affected feature.
Container registry and build trust · current lesson
Registry identities, build tokens, and image provenance are separate controls. Docker’s 2026 Trivy incident guidance describes malicious images distributed after a supplier pipeline compromise. A registry hosting an image does not establish that its build process or contents are trustworthy. This current example replaces the earlier account-count summary of Docker Hub’s 2019 incident.
Twilio · 2022
Twilio reported employee-targeted social engineering that exposed credentials and permitted access to some customer information. Protect support and administrative workflows with strong authentication, constrained privileges, and response procedures for stolen sessions as well as stolen passwords.
Lapsus$ and related groups · 2022
The Cyber Safety Review Board examined attacks involving social engineering, account compromise, and weaknesses in identity and support processes. Defensive priorities include resilient recovery procedures, stronger authentication, and controls over help-desk actions and privileged access.
Okta support system · 2023
The 2023 support-system incident is separate from the 2022 third-party support incident. Okta expanded its findings after the initial November report, including a downloaded customer contact report. Sanitize diagnostic files, protect support-system identities, and revoke exposed sessions or tokens where indicated.
MOVEit / CL0P · 2023
Attackers exploited a SQL-injection vulnerability in MOVEit Transfer for data theft and extortion. The example concerns a managed file-transfer application and its deployments; it should not be generalized into a failure of all cloud storage tenants. Inventory exposed applications and follow vulnerability-specific response guidance.
Snowflake customer environments / UNC5537 · 2024
Mandiant documented theft using previously stolen customer credentials, with missing MFA and other weaknesses in the investigated environments. Its account does not establish a breach of Snowflake’s underlying platform. Reduce credential lifetime, enforce strong authentication, and investigate unusual warehouse access and data export.
Exchange Online · 2023, reviewed in 2024
The CSRB investigated the Summer 2023 intrusion and identified provider security failures. This case is a necessary counterweight to the assumption that all cloud incidents originate in customer misconfiguration. Assess provider assurance, signing-key protection, tenant logging, and response transparency.
Apply the lessons
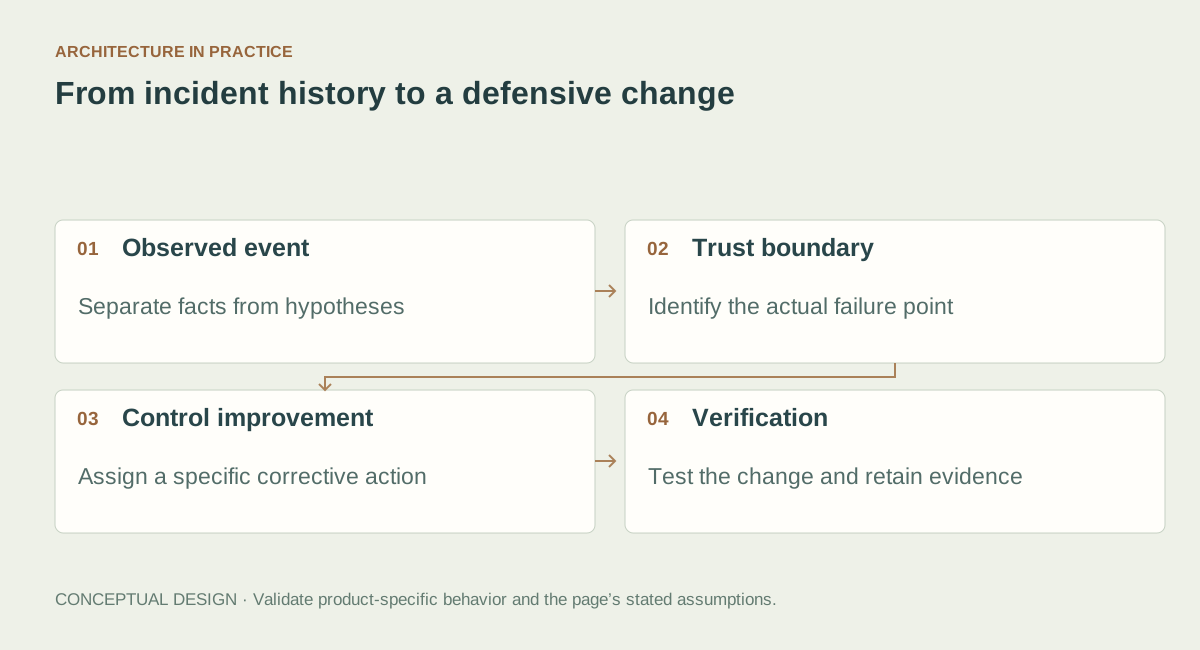
- Identify the actual trust boundary and responsible owner.
- Use short-lived, scoped identities and strong authentication.
- Verify software provenance and separate build from deployment authority.
- Retain useful audit evidence and test incident investigation paths.
- Exercise restoration and identity recovery with your providers.
Practical architecture guides
Cloud Incident Response & Recovery — Turn incident lessons into an executable response plan: detect, investigate, contain, recover, and improve—with evidence and authority defined before the incident.