Governance, Risk, and Compliance for the Cloud
Strong cloud security begins with clear accountability. This section connects governance frameworks, control objectives, risk decisions, continuous assurance, and provider-native evidence so organizations can move quickly without losing oversight.
Building Trust and Control in the Cloud Era
As organizations accelerate their migration to the cloud, the traditional boundaries of governance and control have shifted dramatically. Infrastructure, applications, and data now span multiple platforms and jurisdictions — making Governance, Risk, and Compliance (GRC) more critical than ever. To manage this complexity, enterprises are increasingly turning to cloud-based GRC solutions that deliver real-time visibility, automation, and scalability across their digital ecosystem.
What Is Cloud-Based GRC?
Governance, Risk, and Compliance (GRC) is a structured approach that aligns IT and business processes to organizational objectives while managing risk and ensuring regulatory compliance.
When GRC is delivered as a cloud-based service, it centralizes these functions into an integrated, accessible, and continuously updated platform.
In essence, a cloud GRC platform provides:
Governance: Unified policies, controls, and reporting frameworks across cloud and on-prem environments.
Risk Management: Centralized risk identification, assessment, and mitigation tracking with real-time dashboards.
Compliance: Automated mapping to frameworks such as ISO 27001, SOC 2, GDPR, HIPAA, or FedRAMP, with continuous monitoring and audit readiness.
Why the Shift to Cloud-Based GRC
Traditional GRC systems were often fragmented, manual, and slow to adapt. In contrast, cloud GRC platforms bring key advantages:
Scalability and agility – Rapidly adapt to new regulations, acquisitions, or cloud services without complex infrastructure upgrades.
Centralized visibility – Gain a single source of truth for policies, risks, and compliance posture across hybrid or multi-cloud environments.
Automation and AI insights – Automate control testing, evidence collection, and risk scoring, reducing human error and compliance fatigue.
Continuous monitoring – Integrate directly with cloud providers (AWS, Azure, GCP) to detect misconfigurations and security drift in real time.
Lower operational overhead – No need for on-prem hardware or manual patching — updates, audits, and reporting are streamlined in the cloud.
Core Components of Cloud GRC Platforms
Most modern platforms share a set of integrated modules:
Policy and Control Management – Create, map, and track adherence to internal and external frameworks.
Risk Register and Assessment Tools – Identify, prioritize, and quantify business and cyber risks.
Compliance Automation – Align evidence collection and audit trails with multiple regulatory standards simultaneously.
Incident and Issue Tracking – Manage remediation workflows, accountability, and reporting in a unified dashboard.
Analytics and Reporting – Visualize compliance status and risk exposure for executives and regulators.
Commonly used cloud GRC tools include ServiceNow GRC, RSA Archer Suite, MetricStream, OneTrust, and AuditBoard, among others.
Challenges and Considerations
Adopting cloud-based GRC isn’t without challenges:
Data sovereignty and privacy: GRC data may include sensitive audit and security information that must remain in specific regions.
Integration complexity: Aligning with diverse IT and business systems requires strong APIs and governance structures.
Change management: Successful implementation demands stakeholder alignment and a culture of compliance across departments.
Vendor dependency: Continuous monitoring of the GRC provider’s own compliance and resilience is crucial.
The Future of GRC in the Cloud
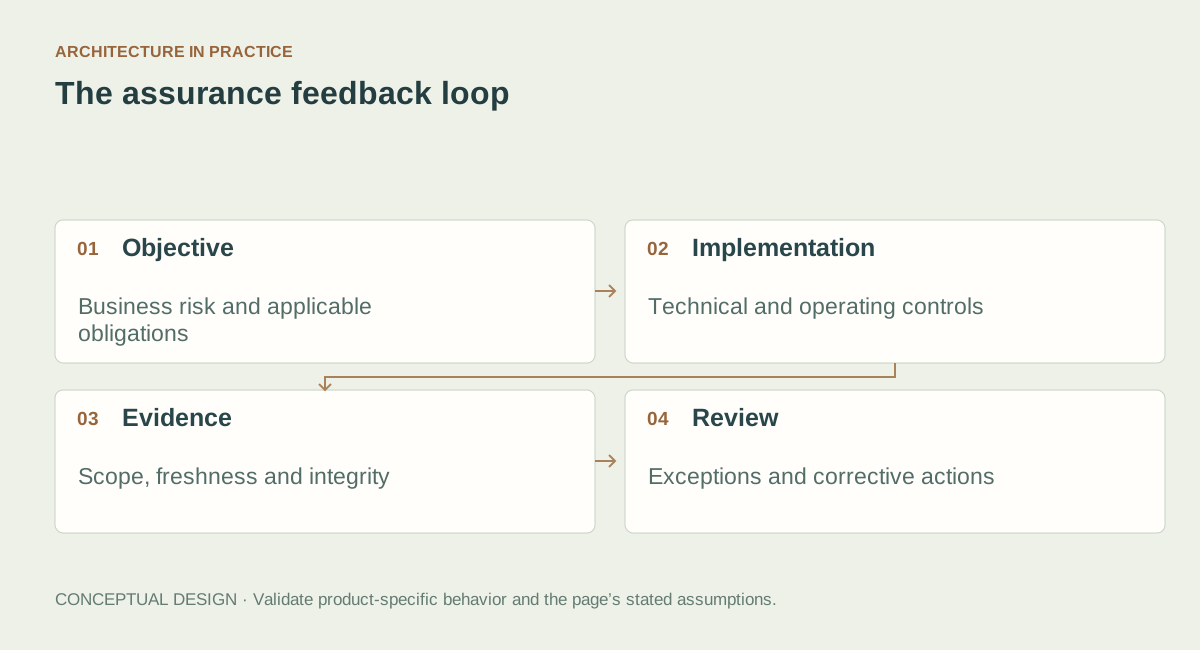
Cloud GRC is evolving toward continuous assurance — where compliance, risk, and governance are not point-in-time exercises but ongoing, automated processes.
Emerging capabilities include:
AI-driven predictive risk analytics
Automated evidence gathering through security telemetry
Integration with zero-trust security frameworks
Unified ESG (Environmental, Social, Governance) and cyber risk reporting
As regulations become more dynamic and threats more sophisticated, cloud-based GRC provides the agility and intelligence needed to maintain trust, resilience, and accountability in an interconnected digital world.
Current guidance · October 25, 2026
Separate laws and contractual requirements from standards, voluntary frameworks, and assurance reports. Automated mappings are starting points; accountable owners must validate applicability, implementation, evidence, and residual risk.
Sources & further reading
Practical architecture guides
Compliance as Code & Continuous Assurance — Connect a control objective to testable implementation, trustworthy evidence, accountable review, and a defined exception process.