Security by Design on Microsoft Azure
Azure security integrates identity, network protection, encryption, posture management, threat detection, and governance. Establish secure landing zones, enforce least privilege through Entra ID, apply Azure Policy, centralize monitoring, and automate remediation.
A High-Level Overview of Azure Cloud Security
As organizations accelerate cloud adoption, Microsoft Azure has emerged as a leading platform for building scalable, resilient, and secure solutions. Azure’s security architecture is built on a multilayered defense model that spans identity, data, network controls, workload protection, DevSecOps, and continuous governance. Together, these components form a comprehensive security ecosystem designed to safeguard applications, infrastructure, and sensitive information across hybrid and multi-cloud environments.
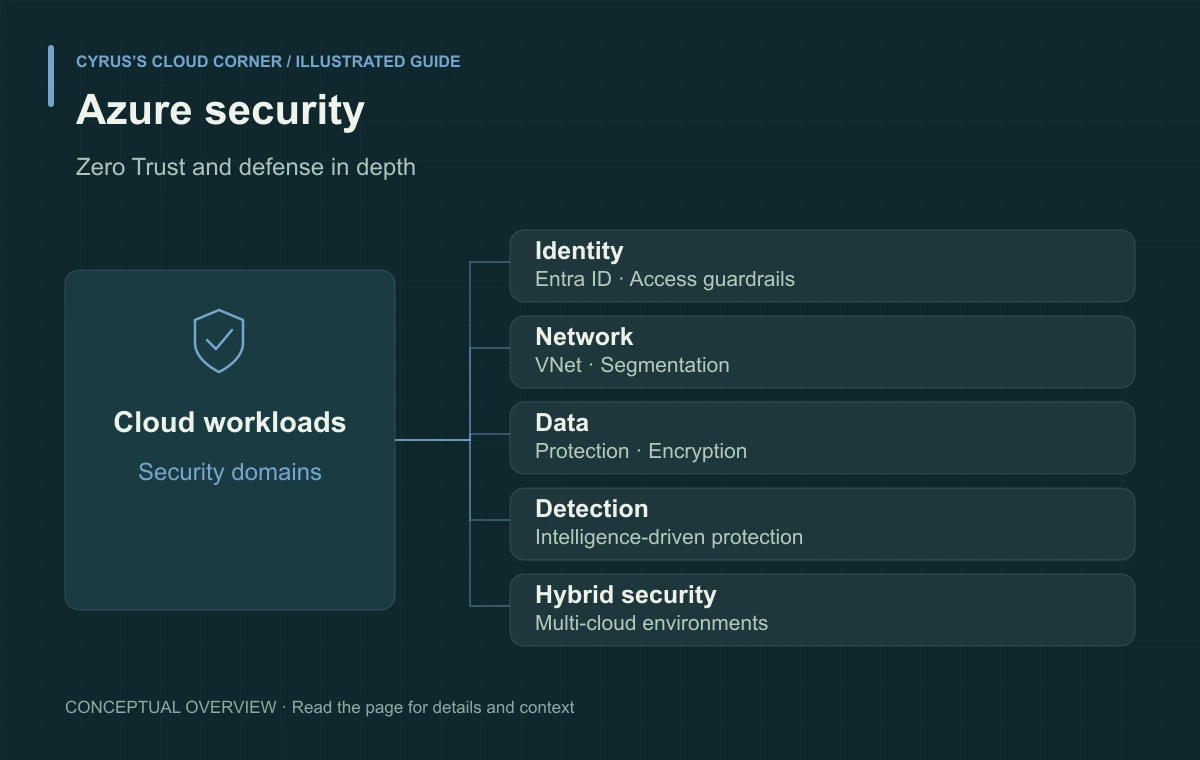
This article provides a high-level overview of Azure Cloud Security, its foundational principles, core services, and recommended guardrails for enterprises.
Azure’s Cloud Security Philosophy
Microsoft’s security strategy is anchored around four pillars:
1. Zero Trust as the Default
Azure assumes breach by default and requires verification at every step. Every identity, device, and workload must authenticate and be authorized before accessing resources.
2. Defense in Depth
Security is implemented at every layer—identity, perimeter, network, data, compute, application, and monitoring—to provide multiple lines of defense.
3. Intelligence-Driven Protection
Microsoft combines threat intelligence with service telemetry to support detection and response. Coverage depends on the services, licenses, data connectors, and configuration actually deployed.
4. Hybrid and Multi-Cloud Security
Azure security tools are not limited to Azure—they extend across on-premises datacenters, AWS, GCP, and edge environments.
Core Components of Azure Cloud Security
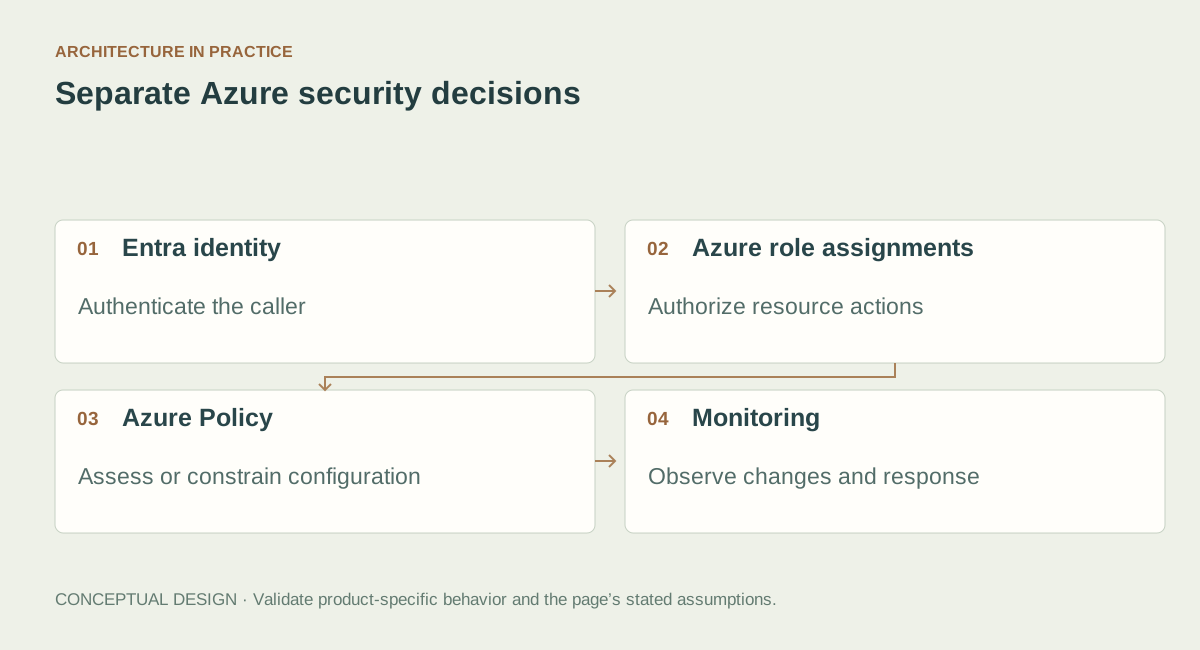
1. Identity and Access Management
Azure relies heavily on identity as the security perimeter.
Microsoft Entra ID (formerly Microsoft Entra ID)
Centralized identity provider for users, services, devices
MFA, Conditional Access, identity governance
Single Sign-On across SaaS, PaaS, and on-prem environments
Privileged access controls via Privileged Identity Management (PIM)
Key Identity Guardrails
Enforce MFA for all users
Implement conditional access policies (device, location, risk-based)
Limit standing admin privileges through PIM
Use Managed Identities for workloads
2. Network Security
Azure Virtual Network (VNet) & Subnet Segmentation
Foundational isolation layer for workloads.
Network Protection Services
Azure Firewall – managed, stateful firewall with threat intelligence
Web Application Firewall (WAF) – protection for web apps via Application Gateway or Front Door
DDoS Protection Standard – absorbs volumetric attacks
Network Security Groups (NSGs) – L4 inbound/outbound rules
Private Endpoints – eliminate public internet exposure
Recommended Guardrails
Hub-and-spoke network architecture
Deny-all/allow-by-exception NSGs
Require private endpoints for PaaS services
Use Azure Firewall for centralized egress control
3. Data Security
Data Protection Tools
Azure Key Vault – secrets, keys, and certificate management
Confidential Computing – secure enclaves for sensitive workloads
Storage Service Encryption (SSE) – default encryption at rest
Azure Disk Encryption – encrypt VM disks using BitLocker / DM-Crypt
Data Governance
Purview (Data Governance) – classification, lineage, and data discovery
Information Protection – labeling and policy enforcement
Recommended Guardrails
Store secrets only in Key Vault
Enable soft delete for Key Vaults, Storage, SQL
Enforce Azure RBAC for access to sensitive data
4. Application & Workload Security
Secure Build & Deployment
GitHub Advanced Security
Azure DevOps with policy-driven build pipelines
Container scanning and artifact signing
Runtime Protection
Microsoft Defender for Cloud – threat detection for VMs, containers, PaaS
App Service Environment (ASE) – isolated hosting for secure workloads
Managed Identities – eliminate secrets in code
Serverless & PaaS Controls
Restrict Function Apps and App Services to private endpoints
Use API Management to secure APIs (OAuth2, policies, rate limiting)
5. Resource Governance & Compliance
Azure Policy
Controls the configuration and compliance of Azure resources at scale. Examples:
Require tags
Allow only approved VM SKUs
Enforce encryption
Require private networking
Azure Deployment Stacks, template specs, and Azure Policy
Standardized environments for regulated workloads.
Regulatory Compliance
Azure maintains certifications for:
FedRAMP, DoD, CJIS
HIPAA, HITRUST
PCI-DSS
ISO 27001/27017/27018
GDPR compliance frameworks
Recommended Guardrails
Use Azure Policy to enforce baseline controls
Block subscription creation outside governance OU
Deploy Landing Zones using Infrastructure-as-Code
6. Monitoring, Detection & Response
Azure Monitor
Central platform for metrics, logs, and alerts.
Log Analytics Workspace
Event aggregation for Azure, hybrid, and multi-cloud.
Microsoft Sentinel
Cloud-native SIEM & SOAR with:
Behavioral analytics
Threat intelligence correlation
Automated playbooks (Logic Apps)
Defender for Cloud
Unified vulnerability management, compliance scoring, and threat detection.
Recommended Guardrails
Enable Defender for Cloud across all subscriptions
Centralize logging in a single workspace
Use Sentinel for SOC analytics and automation
Azure Security Architecture for the Enterprise
A typical secure Azure environment uses:
Landing Zones following the Cloud Adoption Framework (CAF)
Central identity with Conditional Access
Hub-and-spoke network model
Azure Policy for governance
Managed Identities for apps
Defender for Cloud + Sentinel for detection
Automated remediation and IaC guardrails
This blend ensures consistent and scalable security across teams and workloads.
Conclusion
Azure provides a robust, comprehensive suite of security capabilities built for modern cloud architectures. With identity-driven controls, advanced threat detection, enterprise governance tools, and multi-cloud support, Azure enables organizations to build secure, compliant, and resilient environments at global scale.
The foundation of Azure Cloud Security is not just tooling—it’s the operational model: Zero Trust, continuous monitoring, automated governance, and consistent control across hybrid environments. Organizations that adopt these principles and implement Azure’s security services effectively can achieve a strong security posture while accelerating innovation in the cloud.
Current guidance · October 25, 2026
Blueprints is in phased retirement as of this review. The current final retirement date is January 31, 2027. Verify the detailed phase restrictions and export existing definitions before completing migration. Security capabilities and licensing vary by deployment.