Security by Design on Google Cloud
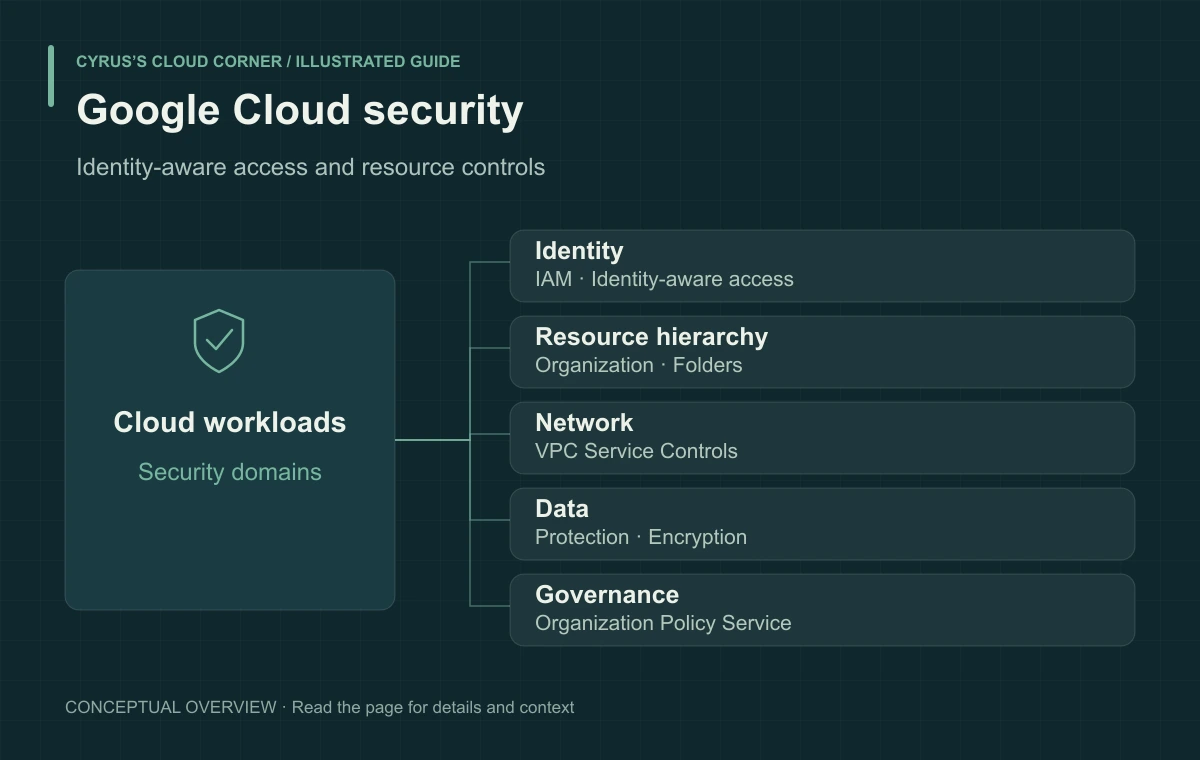
GCP security centers on identity-aware access, resource hierarchy, secure networking, data protection, threat detection, and policy automation. Use least privilege, organization policies, VPC Service Controls, centralized telemetry, and continuous posture management to reduce risk at scale.
Securing the Cloud with Google Cloud Platform (GCP)
Services, Guardrails, and Best Practices
Services, Guardrails, and Best Practices
Security has always been a cornerstone of Google Cloud Platform (GCP). Built upon the same infrastructure that powers Google Search, Gmail, and YouTube, GCP offers a defense-in-depth approach—combining secure-by-design infrastructure, intelligent threat detection, and powerful governance tools.
This article provides an overview of GCP’s core security philosophy, key services and features, and the guardrails that enable organizations to maintain compliance and control at scale.
1. The Google Cloud Shared Responsibility Model
GCP follows the Shared Responsibility Model, similar to other major cloud providers, where both Google and customers share security duties:
Google protects its infrastructure; customers configure identities, workloads, data access, and application controls according to the services used. Compliance reports and authorizations have defined scopes. GDPR is a legal framework, not a security certification granted to an entire cloud platform.
This model ensures that while Google protects the global infrastructure, organizations retain control over their configurations and access models.
2. Core GCP Security Services and Features
GCP’s security framework is designed around four key pillars: identity and access, data protection, threat detection, and governance.
Identity and Access Management
Cloud Identity and Access Management (IAM): Offers granular control over who can access specific GCP resources and what actions they can perform. Roles can be predefined, custom, or resource-specific.
Cloud Identity: A standalone identity-as-a-service platform that integrates with enterprise directories for single sign-on (SSO) and multi-factor authentication (MFA).
Chrome Enterprise Premium (Zero Trust): Implements Google’s zero-trust model, ensuring access decisions are based on user identity, device health, and context—not just network location.
Workload Identity Federation: Allows workloads running outside GCP (like on-premises or AWS) to securely access GCP resources without long-lived service account keys.
Network and Infrastructure Security
Virtual Private Cloud (VPC): Enables isolation of resources, control of network traffic via firewall rules, private service access, and VPC Service Controls.
Cloud Armor: Provides DDoS protection and WAF capabilities for applications deployed on GCP.
Identity-Aware Proxy (IAP): Controls access to web applications and VMs based on user identity and context, without requiring a VPN.
Private Google Access: Ensures that resources without public IPs can securely reach Google APIs and services through the private network.
Network Service Tiers: Allow organizations to choose between premium and standard global network routing for security and performance optimization.
Data Protection and Encryption
Cloud Key Management Service (Cloud KMS): Enables management of cryptographic keys with options for customer-managed and external keys.
- Cloud HSM supplies hardware-backed key protection. Verify the current module validation and service configuration rather than assuming one FIPS version applies to every deployment.
Secret Manager: Securely stores and manages secrets, API keys, and passwords with built-in versioning and IAM integration.
- Confidential Computing adds protection for data in use through supported hardware and execution environments. Available technologies, threat models, and operational requirements vary by machine family and service.
- Cloud Storage encrypts stored objects and supports access, retention, and key-management controls. Bucket Lock and Object Retention Lock address retention; they do not replace IAM, key protection, or recovery planning.
- Sensitive Data Protection provides inspection and transformation capabilities for sensitive information. Configure supported detectors, sampling, locations, and workflows for the data being assessed.
Threat Detection and Monitoring
Security Command Center (SCC): GCP’s unified security management and risk platform—aggregates findings from services like Web Security Scanner, Cloud DLP, and Event Threat Detection. (Available in Standard and Premium tiers.)
Event Threat Detection: Uses Google’s threat intelligence and analytics to identify suspicious activity (e.g., brute force attempts, crypto-mining, or IAM anomalies).
Cloud Logging and Cloud Monitoring: Collects and analyzes logs across infrastructure, providing full visibility for operations and security teams.
Cloud Audit Logs: Records administrative, data access, and system events for governance and forensics.
Google Security Operations Security Operations (Google Security Operations): A cloud-native SIEM and SOAR solution for enterprise-scale threat detection and response.
Container and Kubernetes Security:
Binary Authorization: Ensures only trusted container images are deployed.
GKE Autopilot Security: Provides automated patching, node isolation, and workload identity integration.
3. Governance, Compliance, and Guardrails
GCP integrates policy management, organization-level controls, and compliance automation to maintain secure and auditable environments.
Organization Policy Service
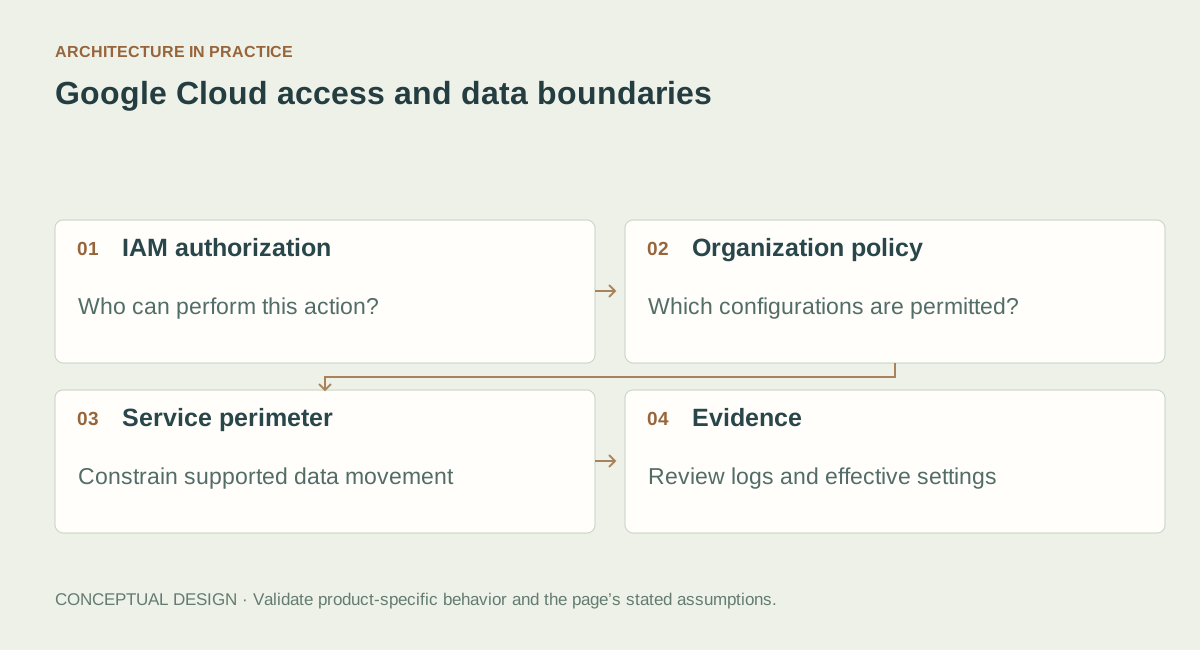
Allows administrators to define and enforce centralized policies (e.g., disallow public IPs, restrict resource regions, or mandate encryption).
Resource Hierarchy and Folders
Enables a structured, scalable management model where policies cascade from organizations → folders → projects → resources.
VPC Service Controls
A powerful security feature that establishes perimeters around data services, preventing data exfiltration risks and enforcing zero-trust boundaries.
Assured Workloads
Assured Workloads helps configure selected control packages and residency constraints. Customers remain responsible for applicable controls, workload configuration, and evidence; the service does not automatically establish legal compliance.
Policy Intelligence
Provides automated insights and recommendations to simplify policy management and reduce overprivileged IAM access.
4. Compliance, Transparency, and Trust
Google Cloud is independently audited and certified for numerous frameworks, including:
ISO 27001 / 27017 / 27018
SOC 1, 2, and 3
FedRAMP High
HIPAA
GDPR
PCI DSS
Cloud Compliance Reports Manager provides on-demand access to audit artifacts and certifications for customer verification.
Additionally, GCP’s Access Transparency and Access Approval features give customers visibility and control over Google’s administrative access to their resources—an industry-first for cloud transparency.
5. GCP Security Best Practices
Implement Zero Trust with Chrome Enterprise Premium to secure user and workload access.
Use IAM best practices: apply least privilege, avoid service account key sprawl, and leverage groups for consistent access control.
Automate policy enforcement using Organization Policies and SCC.
Encrypt everywhere: enforce encryption at rest, in transit, and in use.
Monitor continuously: integrate Security Command Center, Logging, and Google Security Operations for comprehensive detection and response.
Apply data perimeters with VPC Service Controls to prevent cross-boundary data movement.
6. Key Security Resources
Google Cloud Security Foundations Guide – official blueprint for secure GCP deployments.
Security Command Center Documentation – detailed guide for implementation and integrations.
GCP Compliance Resource Center – access to certifications, attestations, and reports.
Google Cloud Security Blog – updated insights, threat research, and best practices.
Conclusion
Google Cloud Platform’s security architecture is grounded in decades of Google’s operational excellence and zero-trust innovation. With its blend of automated guardrails, intelligent detection, and customer-centric transparency, GCP empowers organizations to innovate securely while meeting even the strictest regulatory standards.
By leveraging GCP’s integrated suite of security services—spanning identity, network, data, and compliance—organizations can confidently build and operate resilient cloud environments, knowing security is woven into every layer of their infrastructure.
Current guidance · October 25, 2026
VPC Service Controls constrain data movement for supported services; they are not a replacement for IAM or a general network firewall. Provider attestations are scoped evidence and do not establish a customer workload’s compliance with a law such as GDPR.