Applying the CSA Cloud Controls Matrix
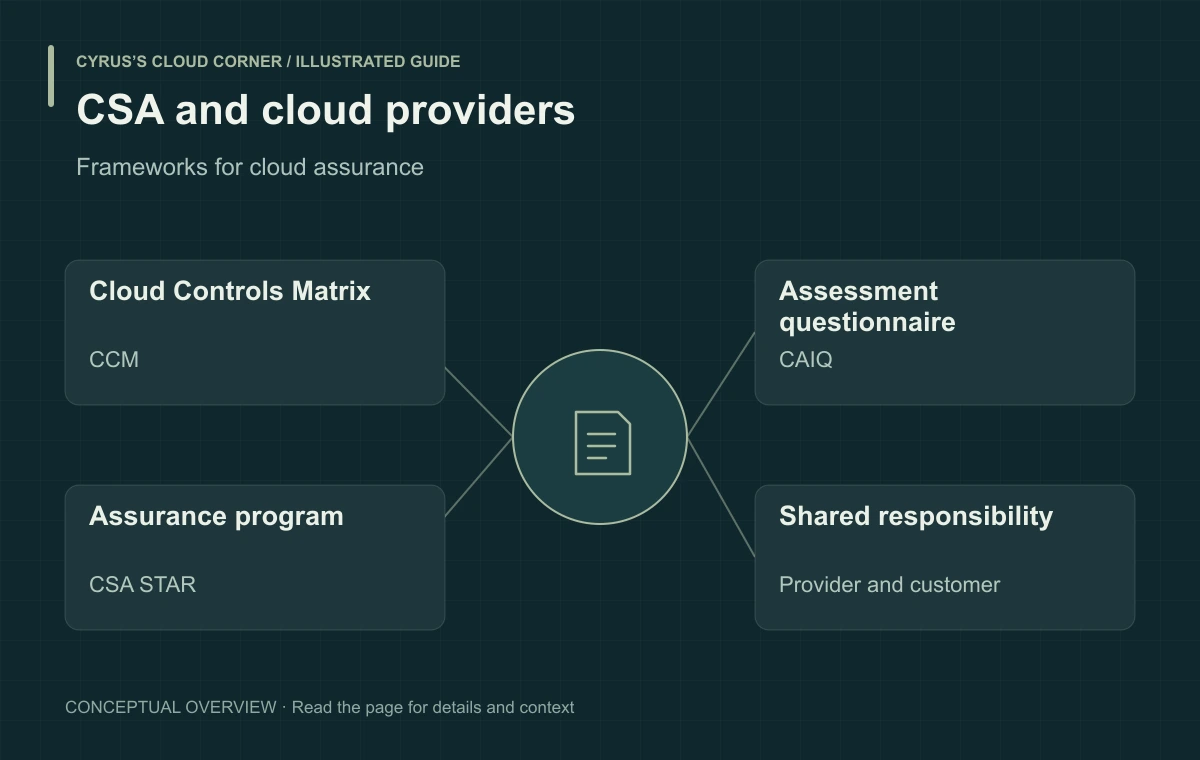
The CSA CCM translates cloud risk into control domains that can be mapped across AWS, Azure, and Google Cloud. Useful mappings distinguish provider responsibility from customer responsibility and connect policies to configurations, telemetry, evidence, exceptions, and continuous assurance.
How the Cloud Security Alliance Strengthens CloudSec: Control Mappings, CSP Alignment, and Risk Governance
As cloud adoption accelerates, organizations increasingly rely on authoritative, vendor-neutral security frameworks that can help them understand, measure, and improve their cloud security posture. The Cloud Security Alliance (CSA) plays a central role in this ecosystem by providing industry-driven best practices, control catalogs, maturity models, and assurance programs designed exclusively for cloud computing.
While Cloud Service Providers (CSPs) such as AWS, Microsoft Azure, and Google Cloud Platform (GCP) deliver the infrastructure and native security tools, CSA frameworks help translate cloud risks into standardized security controls and measurable governance practices. This alignment makes CSA one of the most critical organizations in modern cloud security.
1. What is the Cloud Security Alliance (CSA)?
The Cloud Security Alliance is a global, nonprofit organization dedicated to defining and raising awareness of best practices for secure cloud computing. Unlike NIST—which spans a wide spectrum of cybersecurity—CSA focuses exclusively on cloud environments.
CSA delivers:
Cloud Controls Matrix (CCM) – A comprehensive control framework for cloud security
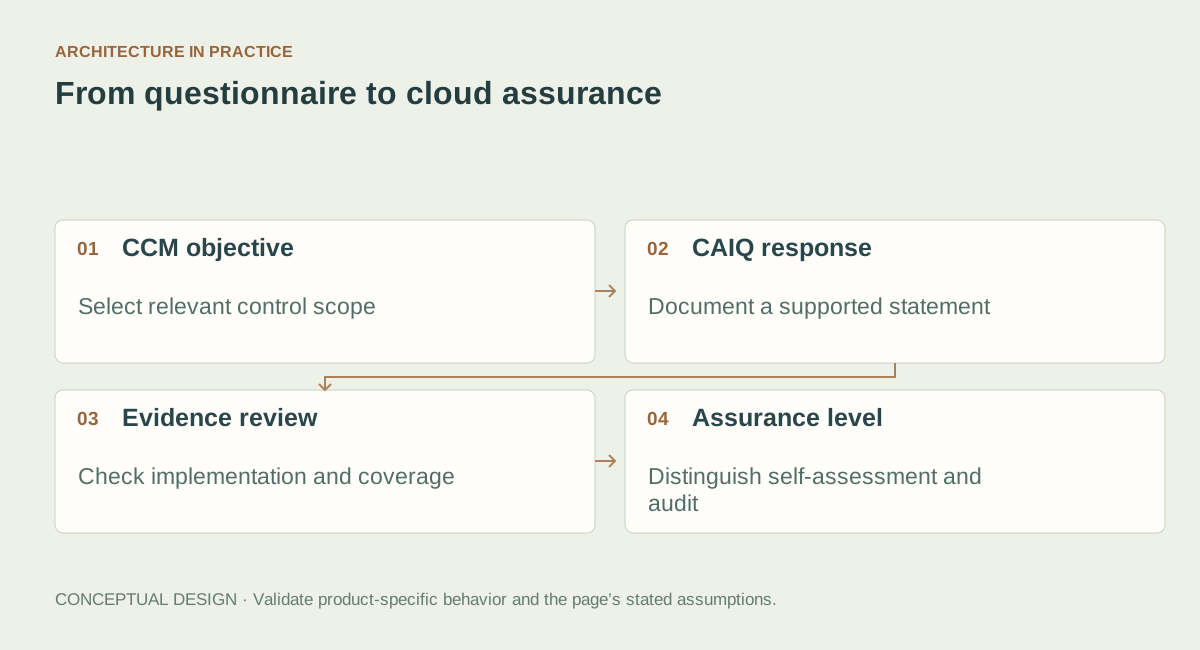
CAIQ (Consensus Assessment Initiative Questionnaire) – A standardized questionnaire for assessing CSP security
STAR Registry (Security, Trust, Assurance, and Risk) – A public, transparent cloud provider assurance program
CCSK (Certificate of Cloud Security Knowledge) – The leading cloud security certification
Top Threats to Cloud Computing – Industry-recognized threat intelligence
IoT, container, and zero-trust guidance
CSA frameworks are globally recognized across government, enterprise, healthcare, and critical infrastructure.
2. CSA and the Shared Responsibility Model
Like NIST, CSA frameworks align tightly with the shared responsibility model used by all major CSPs:
CSP Responsibilities Include:
Data center physical security
Underlying compute, storage, and network infrastructure
Hypervisor security
Managed service platform security
Global DNS, CDN, and backbone network protections
Customer Responsibilities Include:
Identity & access management
Network configuration and segmentation
Workload protection
Encryption usage and key management (unless managed)
Monitoring, logging, and threat detection
Data classification and lifecycle management
CSA frameworks help organizations map these responsibilities to specific controls, documentation, and risk assessments.
3. CSA’s Core Frameworks and How They Map to CSPs
⭐ Cloud Controls Matrix (CCM)
CSA’s flagship security control framework for cloud computing.
It includes 197 controls across 17 domains, such as:
IAM (Identity & Access Management)
Infrastructure & Virtualization Security
Cryptography & Key Management
Data Governance
Audit, Compliance, & Monitoring
Threat & Vulnerability Management
Application & API Security
Business Continuity
What makes CCM special is that it is:
Cloud-specific
Control-rich and detailed
Fully mapped to major standards
CCM maps to:
NIST SP 800-53
ISO 27001/27017
CIS Controls
PCI DSS
FedRAMP
SOC 2
COBIT
ENISA guidelines
And importantly, each CCM domain directly maps to AWS, Azure, and GCP’s native services.
Example CCM mapping:
CSA CCM Control
Example CSP Service Alignment
IAM-01: Identity Management ==> AWS IAM, Microsoft Entra ID, GCP IAM
DSI-02: Data Retention Policies ==> S3 lifecycle rules, Azure Blob lifecycle, GCP Object Lifecycle Management
LOG-01: Logging and Monitoring ==> CloudTrail, Azure Monitor, GCP Cloud Logging
TVM-03: Vulnerability Management ==> AWS Inspector, Microsoft Defender for Cloud, GCP Security Command Center
⭐ CAIQ – Consensus Assessment Initiative Questionnaire
CAIQ is a standardized questionnaire (almost a “self-attestation”) that organizations use to assess CSPs and SaaS vendors.
It includes detailed questions about:
Data protection
IAM
Network controls
Monitoring
Incident response
Compliance
Supply chain
Encryption
Tenant isolation
Most CSPs publish their CAIQ responses publicly.
⭐ CSA STAR Program (Security, Trust, Assurance, and Risk)
The CSA STAR Registry is a global assurance program where CSPs publish their controls and audit results.
STAR has three levels:
Level 1 (Self-assessment) – CAIQ + CCM mapping
Level 2 (Third-party audit) – Often ISO 27001 + CCM
Level 3 (Continuous auditing) – Automated, near-real-time assurance
AWS, Azure, and GCP participate heavily in STAR.
4. CSA’s Cloud Risk and Security Areas
CSA focuses on cloud-unique risks, including:
Top Threats to Cloud Computing
Often called “The Egregious 11,” these include:
Misconfiguration
Lack of cloud security architecture
Identity and access issues
Insider threats
Account hijacking
Weak change control
Limited visibility
Data breach
Insecure interfaces and APIs
Shadow IT
Poor key management
These threats are directly mapped to CCM controls.
5. How CSA Frameworks Improve Cloud Security
1. Standardized Assessment Across CSPs
CSA provides a universal control set that works whether you are using: AWS, Azure, GCP, OCI or SaaS platforms
This improves multi-cloud governance.
2. Enhanced Cloud Governance and Compliance
CCM controls serve as a cloud-adapted baseline for:
Access control
Encryption
Network security
Virtualization and container security
DevSecOps
Logging and telemetry
Supply chain risk
Data governance
Organizations can use CCM as a policy and audit backbone.
3. Support for Zero Trust
CSA provides cloud-specific Zero Trust guidance, mapping to:
Identity-first architectures
Continuous authorization
Micro-segmentation
Context-aware access
API-level security policies
4. Secure Cloud Architectures
CSP security reference architectures commonly map directly to CSA controls.
Examples:
AWS Well-Architected Framework → CSA CCM
Azure Cloud Adoption Framework → CCM/CAIQ
GCP Architecture Framework → CCM/STAR mappings
This ensures architectures can meet compliance in sectors like:
Finance
Healthcare
Government
Critical infrastructure
5. Transparent Vendor Risk Assessment
CAIQ + STAR provides visibility into:
CSP data handling
Encryption standards
Access control mechanisms
Tenant isolation
Secure SDLC practices
Incident response capabilities
This accelerates vendor onboarding and reduces third-party risk.
Conclusion: Why CSA is Critical for Securing the Cloud
As organizations expand their cloud presence, CSA provides the specialized, cloud-native security frameworks needed to manage risk at scale. Through tools like CCM, CAIQ, and STAR, CSA creates a transparent, standardized approach to assessing CSPs and securing cloud workloads.
Together with CSP-native capabilities and the shared responsibility model, CSA helps organizations:
Build secure architectures
Reduce cloud misconfigurations
Validate vendor security
Improve compliance maturity
Strengthen identity, data, and network security
Maintain continuous cloud assurance
CSA is not just a security framework—it is an ecosystem that shapes how organizations design, assess, and secure cloud environments globally.
Current guidance · October 25, 2026
CSA’s CCM page describes 197 control objectives across 17 domains. Pin the actual downloaded release used in an assessment. STAR Level 1 is self-assessment; Level 2 involves third-party certification or attestation. A questionnaire response is not an independent audit opinion.